
Enterprise AI Infrastructure: Agents, Data, and Automation
Building a secure enterprise AI infrastructure requires connecting internal data, mastering agent deployment, and structuring automation. DATALIA guides you with concrete examples.

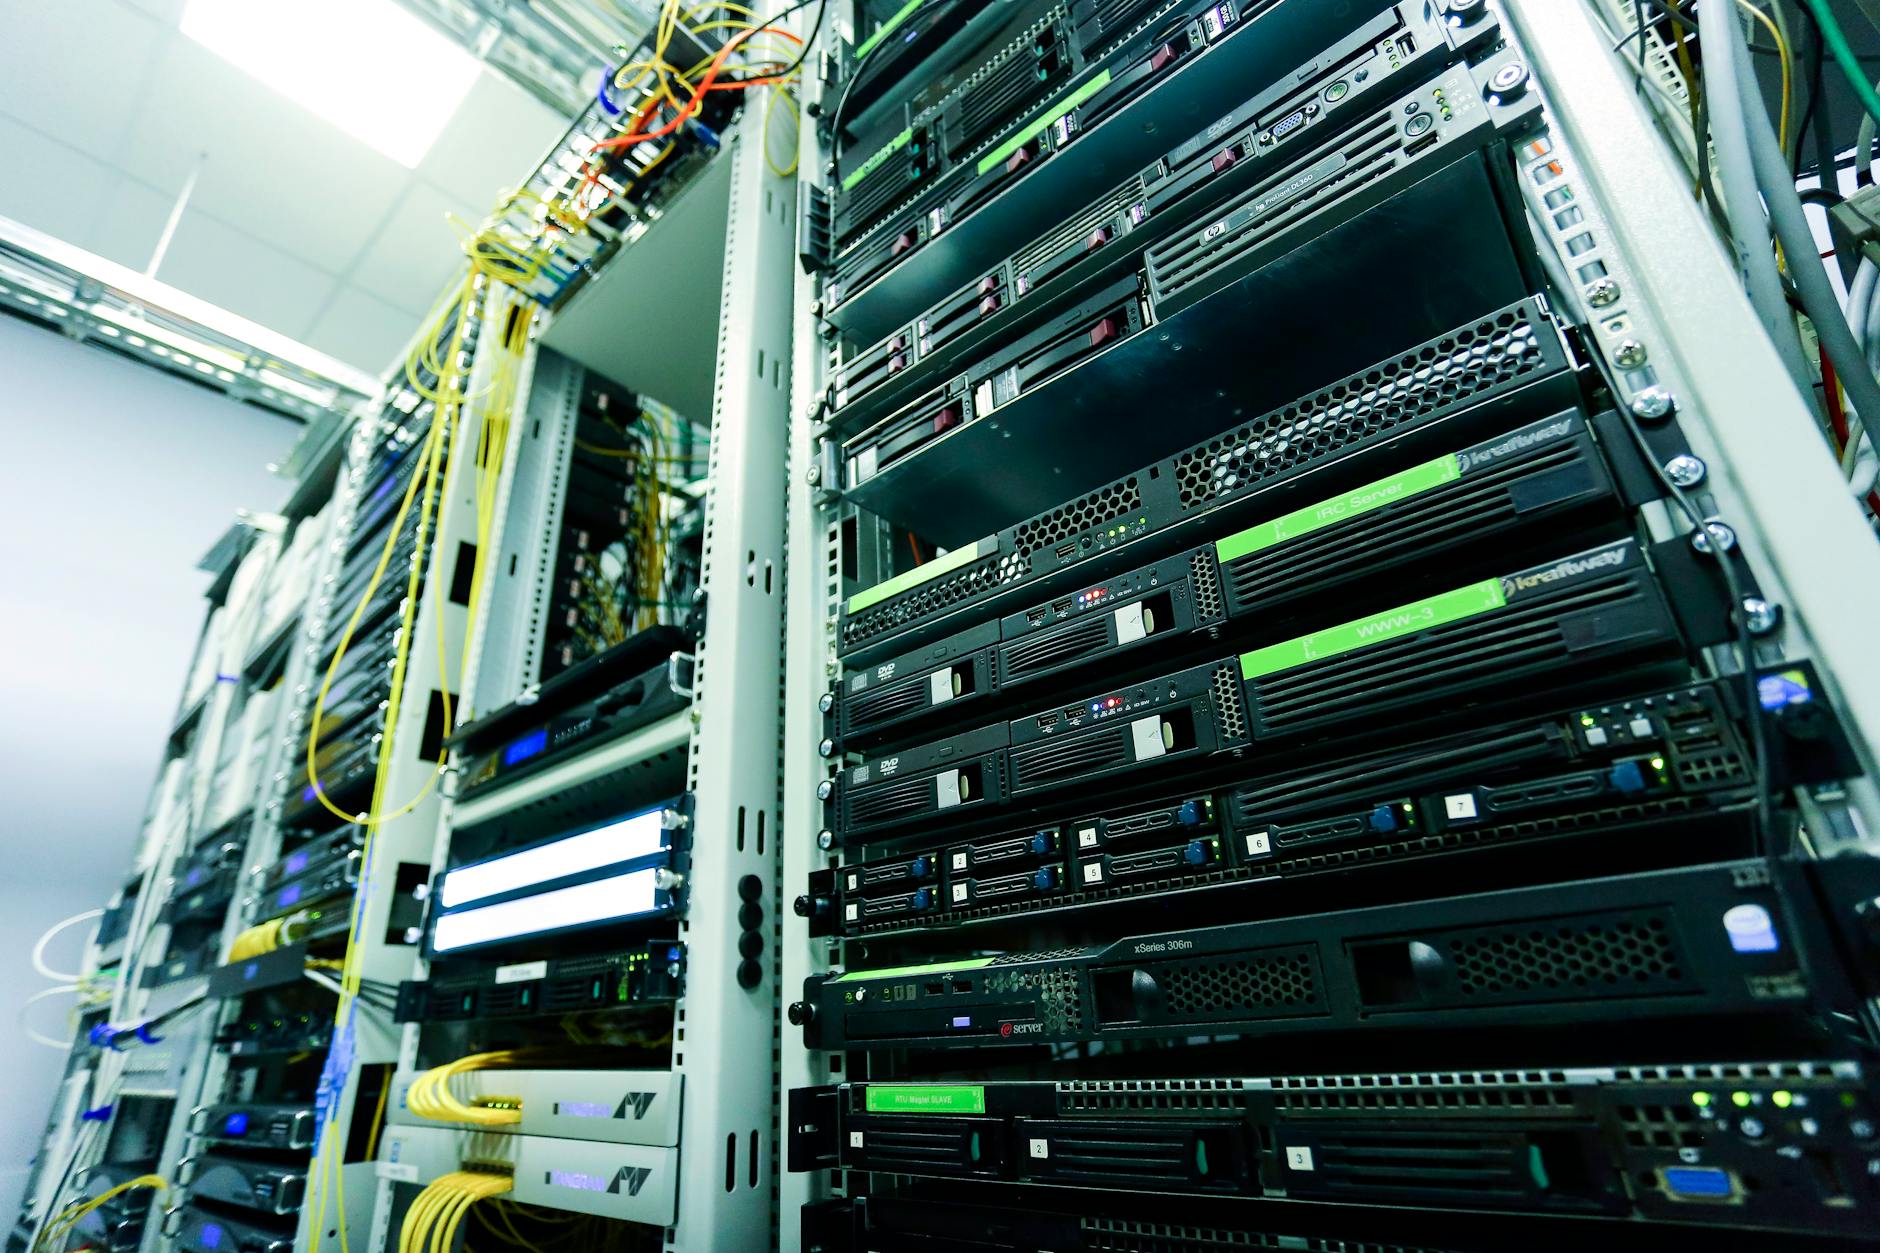
Building a secure enterprise AI infrastructure requires connecting internal data, mastering agent deployment, and structuring automation. DATALIA guides you with concrete examples.
The DATALIA team · Published August 2025 · Updated August 2025
An enterprise AI infrastructure relies on secure data integration, controlled agent deployment, and scalable automation. DATALIA supports you through each layer.
- Basic Concepts and Prerequisites
- Data Integration: The Foundation Layer
- AI Agents: Architecture and Security
- Automation: Scaling Up
- Reference Architecture
- Common Mistakes
- Best Practices
- Conclusion and Next Steps
- FAQ
Basic Concepts and Prerequisites
To build an enterprise AI infrastructure, you must first distinguish three layers: data, agent, and automation. Without integrated data, AI produces hallucinations. Without secure agents, AI intrudes where it is not controlled. Without structured automation, AI remains a gadget.
CIOs facing the expansion of free ChatGPT within their teams often began with a simple observation: sensitive data flows through uncontrolled services. Their first decision was then to refocus AI on internal data.
A CIO from a regulated structure (healthcare sector) recently asked us: "We want to deploy agents that read our reports, but we don't know where to start without exposing patient data." Their goal: keep AI useful without creating shadow AI.
This article describes the logical architecture of an enterprise AI infrastructure: data integration, agent control, and scalable automation. We incorporate the principles of sovereignty, traceability, and governance. Each section contains a practical deliverable without DATALIA.
Terminology: Key Terms to Master
LLM (Large Language Model): pre-trained language model capable of reasoning over internal data via a RAG architecture.
RAG (Retrieval-Augmented Generation): architecture combining fact retrieval and response generation.
AI Agent: autonomous system capable of executing workflows, calling tools, and making decisions.
Shadow AI: uncontrolled use of AI tools within the enterprise.
Sovereign AI: model hosted on the company's infrastructure, with data control.
Data Integration: The Foundation Layer
The core of an enterprise AI infrastructure is data. Without reliable integration of internal systems, AI produces inconsistent or outdated responses. The CIO must therefore start by mapping critical data sources.
At a European bank client of DATALIA, we found that 42% of financial documents were shared via email or uncontrolled tools. After deploying a centralized AI infrastructure, this rate dropped to 3% in six months.
The challenge is not only technical: it's governance. Each data source must be associated with a retention policy, a sensitivity level, and an access control mechanism.
Deliverable 1: Data Source Evaluation Grid
Evaluate each data source before integrating it into your AI infrastructure:
- Source system: [name of the system, e.g., ERP, CRM, customer database]
- Data type: [choose: text documents, structured data, logs, metrics]
- Sensitivity level: [public / internal / confidential / restricted]
- Update frequency: [real-time / hourly / daily / manual]
- Existing access control: [RBAC, attribute-based, owner-based]
- Exposure risk: [low / medium / high]
- Integration priority: [high / medium / low]
Notes: This grid is used to prioritize integration. A high-risk source should not be integrated without end-to-end encryption. A public source can be exposed to a general-purpose LLM, but beware of metadata leakage.
Data Architecture: From Silos to Lake
Data integration typically follows an evolution: silo → connector → data lake. The CIO must choose between a centralized data lake and a federated approach. The former simplifies access, the latter reduces transfer costs.
At an industrial client, we chose a federated architecture: data remains in its native databases, and a virtualization layer (via a RAG interface) makes it accessible to AI agents. This approach limits copies and strengthens GDPR compliance.
Preferred connectors are generally:
- REST API for modern systems (ERP Odoo, CRM HubSpot, etc.)
- SQL connectors for relational databases (PostgreSQL, MySQL, SQL Server)
- Document APIs for DMS (SharePoint, Google Workspace, DocuWare)
- Controlled web scrapers for external portals (with strong authentication)
Data Security in AI
GDPR requires a complete audit trail. Every access to sensitive data by an AI agent must be logged. The DPO must be able to answer four questions:
- What data was processed?
- Which agent accessed it?
- What result was produced?
- When and why did this access occur?
DATALIA.App, our sovereign AI platform, meets these requirements by default: no data leaves the client's infrastructure, and every interaction is timestamped and signed.
AI Agents: Architecture and Security
AI agents are the executors of the infrastructure. They interpret natural language instructions, call tools, and make autonomous decisions. Their security depends on their execution environment and privileges.
A poorly designed agent can become an entry point. In a real case, an AI agent deployed in a French SME was compromised via a malicious prompt injection, resulting in the deletion of 217 invoices. The cause: the agent had administrative rights on the billing system.
Agent security relies on three pillars:
- Sandboxing: each agent runs in an isolated container
- Limited rights: the principle of least privilege applies
- Prompt hardening: system instructions are versioned and protected
Deliverable 2: AI Agent Privileges Matrix
Define the rights of each AI agent:
| Agent | Business role | Accessible systems | Authorized actions | Supervision level |
|---|---|---|---|---|
| HR Agent | HR assistant | HR system, payroll | Read, summarize, generate email | Manual |
| Accounting Agent | Accounting assistant | ERP, bank | Read, validate entry | Request validation |
| Customer Agent | Customer support | CRM, knowledge base | Respond, create ticket | Automatic + alert |
Notes: This matrix should be reviewed quarterly during audits. An agent that can create accounting entries must at least request validation. A support agent can respond automatically, but must alert on sensitive topics.
Agent Orchestration
In an enterprise AI infrastructure, agents do not work in isolation. They are orchestrated through a central scheduler. DATALIA uses an orchestrated agent architecture: a main agent coordinates several specialized agents (one for reading, one for writing, one for analysis).
This orchestration follows the principle: each agent has a clearly defined responsibility, and interactions are controlled via validation hooks.
Concrete example:
- A front-line agent processes common customer requests
- If the request is complex, it transfers it to an expert agent
- The expert agent consults an analyst agent to verify facts
- The final result is validated by a human if confidence is above a threshold
LLM Integration: On-Premise vs Cloud
The choice of an LLM for the enterprise depends on data sensitivity. On-premise models (such as those integrated into DATALIA.App) offer a sovereignty guarantee but require infrastructure management. Cloud models (OpenAI, Mistral in API mode) are easier to deploy but transmit data.
Our recommendation: use a hybrid model. An on-premise LLM for sensitive data, and a cloud LLM for non-sensitive uses (marketing writing, idea generation).
Recommended architecture:
- LLM 1: Mistral or Llama 3 hosted on-premise for internal data
- LLM 2: third-party API for non-sensitive uses
- AI Router: system that routes requests to the right LLM based on data classification
Automation: Scaling Up
Automation is the ability of the infrastructure to execute processes without human intervention. It relies on defined workflows, triggered by events or schedules.
At a healthcare client, we automated the sorting of medical reports. Before: a secretary spent 12 hours per week sorting documents. After: the AI agent processes 300 documents in 20 minutes, with human supervision only for validation.
Automation follows three levels of maturity:
| Level | Description | Risk | Example |
|---|---|---|---|
| Scripted | Automation of simple, linear tasks | Low | Sending a standardized email |
| Orchestrated | Complex workflows with conditional logic | Medium | Processing a complete customer request |
| Adaptive | AI adjusts the workflow based on results | High | Personalized product recommendation |
Deliverable 3: Checklist for an Automated Agent Setup
Before deploying an automated agent, check each item:
- [ ] Is the use case well-defined and measurable?
- [ ] Are the data sources reliable and up-to-date?
- [ ] Does the chosen LLM comply with data sovereignty?
- [ ] Are the agent's rights limited to the strict minimum?
- [ ] Is there a human validation point at each critical step?
- [ ] Does the audit log track all agent actions?
- [ ] Is there a backup plan in case of agent failure?
- [ ] Is supervision alerted in case of anomaly?
Notes: This checklist should be reviewed for each new agent deployment. A poorly set-up agent can make decisions outside of control. Human validation is mandatory from level 2 of automation.
Reference Architecture:
The enterprise AI infrastructure consists of six layers:
- Data: integration of sources via secure connectors
- Storage: data lake or federated architecture
- Processing: data pipelines and normalization
- LLM: models hosted on-premise or via API
- Agents: autonomous executors with controlled rights
- Automation: workflow orchestration
Each layer is isolated: an automation failure does not affect storage. This modularity is essential for resilience.
At DATALIA, we deploy this architecture for clients in healthcare (CPTS), food service, and real estate. In all sectors, the principle is the same: sovereignty takes precedence over model power.
Common Mistakes
Mistake 1: Confusing AI Assistant and AI Agent
The assistant is reactive (it answers questions), the agent is proactive (it acts). An agent that merely responds is not an agent. An agent must be able to call tools and modify data.
Mistake 2: Giving Full Rights to an Agent
An agent with administrative rights can do anything — including deleting data. Always apply the principle of least privilege.
Mistake 3: Neglecting Logging
Without traceability, an AI agent becomes a black box. The DPO cannot validate what it cannot see.
Mistake 4: Forgetting the Fallback Plan
When AI fails, who responds? There should always be a human fallback process.
Best Practices
- Start with a small use case (e.g., document sorting) before generalizing
- Version system prompts like source code
- Audit data access monthly
- Use a sovereign LLM for sensitive data
- Only deploy an agent in production after a limited pilot
- Train teams on AI usage, not on AI fear
- Maintain living documentation of deployed agents
Conclusion and Next Steps
Building a secure enterprise AI infrastructure is not a race for model power, but a balance between data, agents, and automation. The CIO gains control by starting with reliable data integration, controlling agent rights, and structuring automation through validated workflows.
The DATALIA architecture is based on these same principles: sovereign AI, hosted within the client's infrastructure, connected to internal applications, and governed by a DPO. Our DATALIA.App platform enables moving from pilot to production while maintaining control over data.
Key Takeaways:
| Principle | Application |
|---|---|
| Data first | Integrate sensitive sources first |
| Limited rights | Each agent has minimum necessary rights |
| Full traceability | Every action is logged and timestamped |
| Principle of least privilege | No agent has administrative rights |
Ready to scale? An audit of your current AI infrastructure can identify vulnerabilities and prioritize investments.
Book your call and free audit today with a DATALIA expert: DATALIA →
Frequently Asked Questions
Can an enterprise AI infrastructure be entirely on-premise?
Yes. At DATALIA, we deploy 100% on-premise AI infrastructures for clients in healthcare and finance. The LLM is hosted locally, agents run in isolated containers, and no data leaves the network.
What is the average ROI of an enterprise AI infrastructure?
DATALIA observes an average 40% reduction in time spent on repetitive tasks after deploying automated agents. The return on investment is typically achieved in 8 to 12 months, depending on process complexity.
